Find the AI tools
nobody approved.
Staff install AI assistants and coding agents on their own. GreyArm shows which ones are on your work computers, where your data goes, and lets you approve or block each one.
AI is already at work.
Did anyone approve it?
A spreadsheet pasted into a free chatbot is a copy of your customer list on someone else’s servers.
Coding agents run commands with the same access as the person who started them — including the credentials on that computer.
You can’t write an AI policy for tools you don’t know are installed. Most small teams have no list at all.
See where your
data is going.
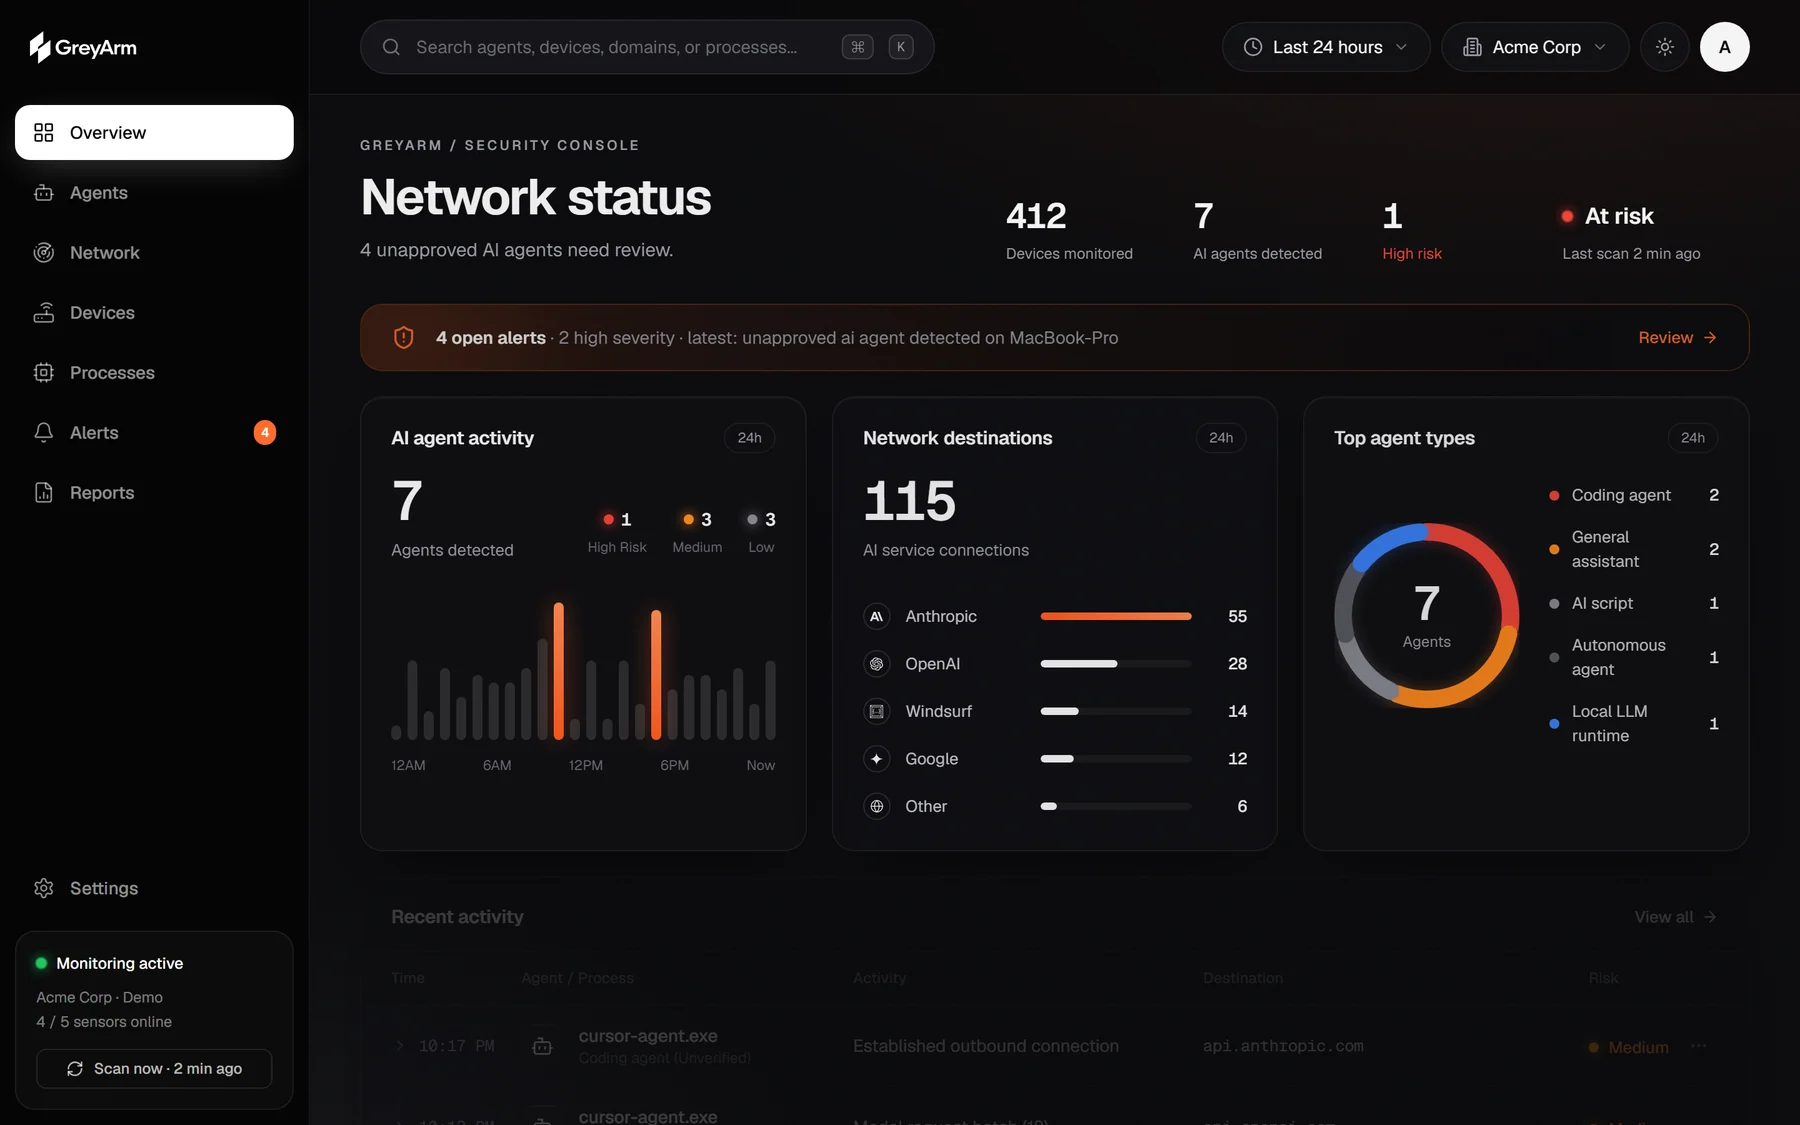
Which work computer, which program, which AI company — and how often. Every finding comes with a risk level and a plain-English explanation, so you know what matters.
A policy you can
actually enforce.
Mark each AI tool approved or blocked. If a blocked tool runs again, you’re alerted straight away.
Stop the program, cut off its AI endpoints, stop it relaunching or take the computer offline — and undo it any time.
Block AI services for every device on the office network, including phones and laptops without the sensor.
Ten documented rules mapped to MITRE ATT&CK, with the process, signer and destinations behind each finding.
Export findings and decisions as CSV or JSON for your records, insurer or auditor, or pull them through the API.
Email and push alerts the moment a new AI tool appears, and approvals from the mobile app.
Oversight without
surveillance.
GreyArm records which program reached which AI service — never what anyone typed, read or asked. Tell your team it’s there; there’s nothing in it you’d be uncomfortable showing them.
How GreyArm handles data